Opens in a new tab
Advanced Identity Manager

Manage, orchestrate and control identities, permissions and credentials across physical and logical security environments, centrally, on one platform.

One Identity Layer
Connects people, identities, credentials and permissions across your entire organization.
Physical & Logical
Buildings, security areas, applications and IT systems, controlled consistently across sites and systems.
Automated Lifecycle
From onboarding to offboarding, the right permissions at every point in time.
What is AIM?

Identity management for physical and logical access.

AIM, short for Advanced Identity Manager, is a PIAM solution that centralizes physical and digital identity management. It connects and integrates your physical environment, including Access and Workplace Management solutions. Whether onboarding new employees, granting secure access or managing authorizations for visitors and external companies, it simplifies the management of your access control by automating approval processes, standardizing authorization models and managing your internal and external identities in one user-friendly interface.

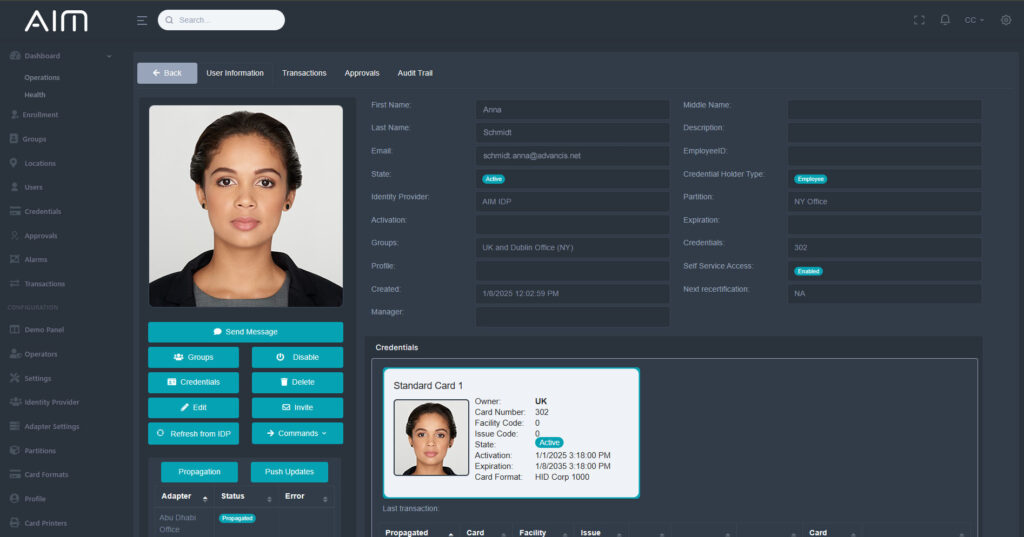
AIM web client showing an identity record with user information, credentials and propagation status across connected systems
  • Central identity management

    Identities and authorizations for employees, suppliers and visitors, managed on one platform without replacing existing hardware.

  • Seamless integration

    Connects your existing security infrastructure, including access control, video surveillance and alarm systems, in one platform.

  • Role-based access control

    Avoid privilege creep by controlling who can do what in a system based on their role: precise, secure and transparent.

  • Automated workflows

    Requests, approvals and recertifications enforce Access Policies and Identity Governance, while real-time alerts and reports support audits and compliance.

The Challenge

Organizations struggle with fragmented systems.

Employees, visitors and external service providers need access to buildings, rooms, applications and servers. As businesses grow, their security needs evolve, often outpacing the capabilities of their existing systems. Organizations often lack visibility into which users are managed in which systems and who has access to what across the estate.  What organizations need is one central way to manage identities and access rights.

  • Manual processes

    Requests travel through e-mails, tickets and paper forms, creating one manual handoff after another.

  • Security risks

    Orphaned accounts and stale permissions stay live long after they should.

  • No transparency

    Nobody can say with certainty who has access to what, or why.

  • Growing admin effort

    Every identity change means duplicate work in every system it touches.

How AIM Works

AIM ensures the right person has the right access at the right time.

AIM works with your existing infrastructure to integrate identities from IT, HR, ERP or visitor management, bringing them together centrally. AIM can orchestrate and manage who needs access, how they prove their identity, and where they can move within the building: one connected process from identity to access.

Identity Sources

Identities flow in automatically from the systems you already run.

  • HR Systems
  • ERP
  • Entra ID
  • Visitor Management
Advanced Identity Manager

One central platform that connects identities, credentials and permissions, and keeps physical and logical access consistent, transparent and in line with policy.

Identity Management
  • Identity LifecycleJoiners, Movers, Leavers: permissions follow the person, automatically.
  • Identity GovernanceAccess Policies, Role Based and Attribute Based Access, ensuring the correct privileges are assigned to each identity.
  • Identity AwarenessA real-time, centralized view of Multi-system / Multi-departmental access.
Who

Identities

  • Employees
  • Visitors
  • Contractors
  • Service providers

…everyone inside and outside your organization.

What

Credentials

  • Cards & badges
  • Mobile credentials
  • Biometrics
  • License plates

…and any other identification media.

Where

Groups

Physical
  • Buildings
  • Security areas
Logical
  • Applications & cloud services
  • Data repositories

Granted, changed and revoked from one place.

  • Access Control Systems
  • Key Management
  • IT Systems & Applications
Connected Systems

Access rights flow out automatically, and your systems stay connected through AIM-ready adapters.

The Result

Physical & logical access. Managed as one.

Identities, credentials and permissions, intelligently linked into one end-to-end process for secure and efficient access control.

Identity Management

The core elements of AIM.

Automate the identity lifecycle, enforce governance, and always know who has access: the core elements of identity management, built into every AIM deployment.

Identity Lifecycle

Automate every stage of an identity. The moment a role or function changes, AIM provisions matching permissions across all connected systems. It works vendor-independently, with approval workflows and self-service built in.

The Lifecycle
  1. Onboarding

    Day-one access, provisioned automatically.

  2. Role change

    Permissions follow the person.

  3. Offboarding

    Every right revoked, everywhere.

Identity Governance

Security, compliance and traceability: AIM ensures access rights match company policy and stay verifiable at any time.

The Rulebook
  • RBACAccess rights assigned by role
  • ABACRights refined by attributes and context
  • Policy managementRules defined once, enforced everywhere
  • ValidationAssignments checked against the rules
  • RecertificationRights reviewed and re-approved on schedule

Identity Awareness

Comprehensive reporting and analytics answer every audit question before it is asked, making audits and compliance reviews dramatically simpler.

The Audit Trail
  • WhoEvery identity, internal or external
  • WhatEvery door, drive and application
  • WhyThe role or rule that grants it
  • CredentialThe exact badge, key or token
  • Approved byNamed approver, full history
Why AIM

Six reasons to centralize.

  • Centralized control

    Uniform policies for physical and logical access.

  • Automated processes

    Less manual effort across the entire identity lifecycle.

  • Maximum transparency

    Traceable permissions and straightforward audits.

  • Zero-Trust

    Always authenticate, use the principle of least privilege.

  • Open integration

    Connects existing security, IT and identity systems.

  • Future-proof

    Scales from a single site to a global organization.

License Model

One platform. Four tiers.

Every AIM license runs on the same platform. Pick the tier that matches the size of the organization; adapters and users scale up from there.

  • Express

    3Adapters
    3,000Identities
  • Basic

    5Adapters
    5,000Identities
  • Professional

    10Adapters
    25,000Identities
  • Enterprise

    Adapters
    Identities
Product Demo

See WinGuard and AIM in Action.

Request your personal product demo and discover how WinGuard, AIM and AOP can work for your building and security infrastructure. Or browse our datasheets, whitepapers and technical documentation directly.

Show Downloads
Personal Info
SELECT YOUR PREFERRED DATE